Today's briefing

Tuesday 3 November 2026

Hackers crank up supermarket freezers to 50°C in a second wave of attacks across Europe, the UK's NCSC warns of an unprecedented rise in cyber incidents, Brazil's biggest crypto exchange loses tens of millions, Google takes down a 1.3 million-device TV box botnet, plus Synology NAS ransomware, Apple spyware alerts in 99 countries, an exploited Siemens industrial flaw, BTCPay Server wallet drains and a ransomware claim against Michigan State.

9 stories

Hackers turn supermarket freezers up to 50°C in a second wave of attacks across Europe
Image: BleepingComputer
Outage

Hackers turn supermarket freezers up to 50°C in a second wave of attacks across Europe

In the early hours of Monday, attackers remotely changed the settings on fridges and freezers at well over 100 shops in Belgium, Sweden, the Netherlands, Luxembourg, Ireland and Estonia, with some units set to 50°C or switched into defrost mode so that stock spoiled. Chains including Ahold Delhaize, Carrefour Belgium, Spar Colruyt, Intermarché, ICA, Coop and SuperValu confirmed problems at some stores, and an Ikea store in Belgium was also hit. It follows a similar attack in France three weeks ago that the Paris prosecutor says had around 700 victims. Nobody has claimed either attack, and Belgium's cyber agency says it may never be known who was behind it.

Why it matters: This shows how old, internet-connected equipment can cause real-world damage. Reports point to older refrigeration controllers from makers such as Danfoss and Copeland, which the makers say are mostly discontinued and no longer get security updates. Any business with remote-controlled building equipment should make sure it isn't reachable straight from the internet and sits behind a VPN or firewall.
UK's NCSC warns of an 'unprecedented rise' in cyber incidents as AI exposes years of unpatched weaknesses
Image: The Record
Policy

UK's NCSC warns of an 'unprecedented rise' in cyber incidents as AI exposes years of unpatched weaknesses

Launching the National Cyber Security Centre's annual report, its chief executive Richard Horne is warning that the UK could see an unprecedented jump in cyber incidents in the coming months. His point is not that AI has invented new attacks, but that it lets attackers find and exploit long-ignored security holes far faster than before. The report says it is highly likely AI-powered malware will be used in a ransomware attack on UK critical infrastructure by 2028. The government is also putting £70 million into a new centre that will use AI to spot weaknesses across critical infrastructure, and £60 million into the first phase of 'Cyber Shield', a national network of defensive AI agents.

Why it matters: The NCSC's message is that the biggest risk comes from basics: old systems still in use and patches that are available but not installed. For organisations and home users alike, keeping software up to date and replacing kit that no longer gets updates is the most effective step.

Brazil's largest crypto exchange, Mercado Bitcoin, halts withdrawals as more than $46 million drains out
Image: The Record
Breach

Brazil's largest crypto exchange, Mercado Bitcoin, halts withdrawals as more than $46 million drains out

Mercado Bitcoin suspended all deposits and withdrawals on Monday after what it called a security incident. Blockchain security firms say more than $46 million left the platform overnight, although the exchange has not confirmed that figure. It says customers were not harmed and no data was breached, but some blockchain experts dispute this, pointing to funds taken from some customer wallets. Tether says it has frozen about $4.5 million of the stolen money and other platforms have frozen around $2 million more.

Why it matters: It comes just days after the record Binance theft, and is another reminder that crypto held on an exchange is only as safe as that exchange. If you use Mercado Bitcoin, watch for official updates only and be wary of anyone contacting you offering to 'recover' funds.

Google takes down a 1.3 million-device botnet hidden in Android TV boxes, and blames the maker
Image: BleepingComputer
Defence

Google takes down a 1.3 million-device botnet hidden in Android TV boxes, and blames the maker

Google and partners including Japan's National Police Agency have disrupted the 'XCPE' botnet, made up of more than 1.3 million Android TV streaming boxes. Google says Chinese manufacturer Videostrong deliberately built a backdoor into the boxes' firmware and sold access to criminals, who used them for ad fraud and to route other people's internet traffic through owners' home connections. Google also knocked out servers used by more than a dozen related malware families, cutting off at least 10 million more devices, and has banned Videostrong from making certified Android devices. The backdoor is still on the boxes and reinstalls itself if removed.

Why it matters: Cheap, unbranded streaming boxes can come with malware already installed. If you own one, the only real fixes are installing clean firmware or unplugging it from the internet. When buying, stick to well-known brands with Google Play Protect certification.

Synology urges NAS owners to update now as C3RB3R ransomware encrypts outdated devices
Image: BleepingComputer
Ransomware

Synology urges NAS owners to update now as C3RB3R ransomware encrypts outdated devices

Synology has warned that attackers are exploiting an old, already-patched flaw to break into its network storage (NAS) devices running out-of-date DiskStation Manager software, then encrypting the files and demanding a ransom. Victims have been finding their files renamed with a .L0CK3D extension and a ransom note telling them to buy a 'C3rb3r Decryptor'. Synology rarely issues warnings like this; its last was in 2019. More than 380,000 Synology NAS devices are reachable from the internet, according to Shadowserver.

Why it matters: Many homes and small businesses keep family photos and work files on a Synology NAS. Update DSM to the latest version, turn on automatic updates, don't expose the management page to the internet, and keep a separate offline backup, because updating won't recover files that are already encrypted.

Apple warns people in 99 countries they may have been targeted by mercenary spyware
Image: The Record
Threat

Apple warns people in 99 countries they may have been targeted by mercenary spyware

Apple has sent a new round of threat notifications to users it believes were individually targeted by expensive 'mercenary' spyware, with this batch going to people in 99 countries. Recipients who have gone public include a Turkey-based journalist and a Lebanese documentary filmmaker. As usual, Apple does not say who is behind the attacks. A researcher who checked several of the alerts said there was not yet enough evidence to tell which spyware maker was involved.

Why it matters: These attacks target a small number of people such as journalists, activists and politicians, not the general public. If you do get an alert, Apple advises turning on Lockdown Mode and getting expert help. Real Apple alerts never ask you to click links or give your password, and you can confirm them by signing in at account.apple.com.

Attackers exploit a perfect-10 flaw in Siemens industrial IoT gateways to plant backdoors
Image: The Hacker News
Vulnerability

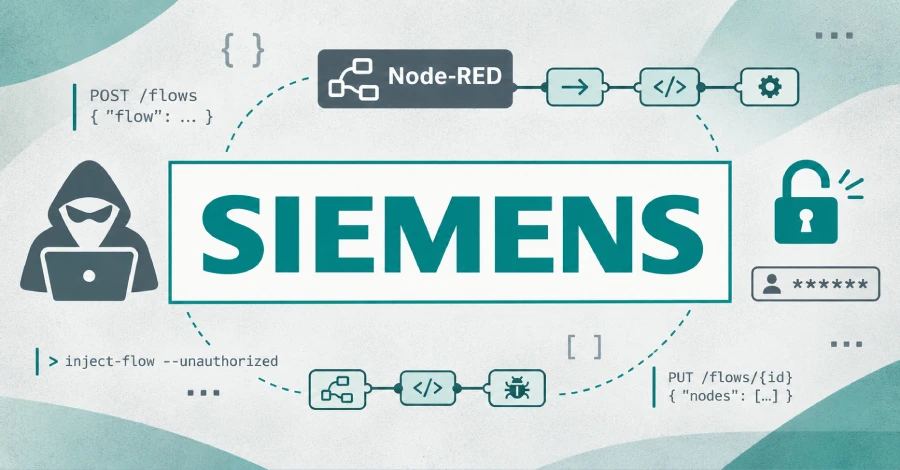
Attackers exploit a perfect-10 flaw in Siemens industrial IoT gateways to plant backdoors

Security firm VulnCheck says attackers have started exploiting a maximum-severity flaw in Siemens SIMATIC IoT2050 Advanced devices, which are used in factories and industrial sites. When the Node-RED automation tool is installed, its web interface did not require a login, letting anyone who could reach it run commands with full control. Since 30 October, attackers have used it to download botnet malware, and some planted hidden web endpoints so they can send commands later. Siemens fixed the bug in August in version 4.3.4.1.

Why it matters: Industrial devices often go unpatched for months. Operators should update, remove Node-RED if they don't use it, or at least put a password on it, and keep these devices off the open internet.

BTCPay Server tells merchants to update now after hackers drain crypto from outdated servers
Image: BleepingComputer
Vulnerability

BTCPay Server tells merchants to update now after hackers drain crypto from outdated servers

The team behind BTCPay Server, free software that lets businesses accept Bitcoin payments on their own servers, says attackers have been emptying 'hot wallets' on installations running version 2.4.1 or older. The attackers were able to log in as an administrator on these older versions. Reports of theft started on Sunday evening, and the project asked hosting providers to take affected servers offline as a precaution. It says it has no credible reports of thefts from servers running the latest version, 2.4.7.

Why it matters: Anyone running BTCPay Server should update to 2.4.7 straight away, or take the server offline if it is on 2.4.1 or older. Self-hosted payment software puts the job of keeping it patched on you.

Ransomware gang behind New Mexico hospital attack claims data on 1.3 million Michigan State students
Image: The Record
Ransomware

Ransomware gang behind New Mexico hospital attack claims data on 1.3 million Michigan State students

The new BYOD ransomware gang, which recently forced the University of New Mexico's hospital to divert ambulances, has listed Michigan State University on its leak site and claims to have personal data on 1.3 million current and former students. The university says the claim relates to suspicious activity it spotted in early October, when it made everyone reset their passwords to new ones at least 15 characters long. MSU says it looked like a possible password compromise and that it has no evidence other data was accessed or stolen. The gang's claim has not been independently confirmed.

Why it matters: If you are a current or former MSU student, be extra wary of emails or calls that mention your studies or ask for personal details. Using a long, unique password and turning on two-step login limits the damage when credentials are stolen.